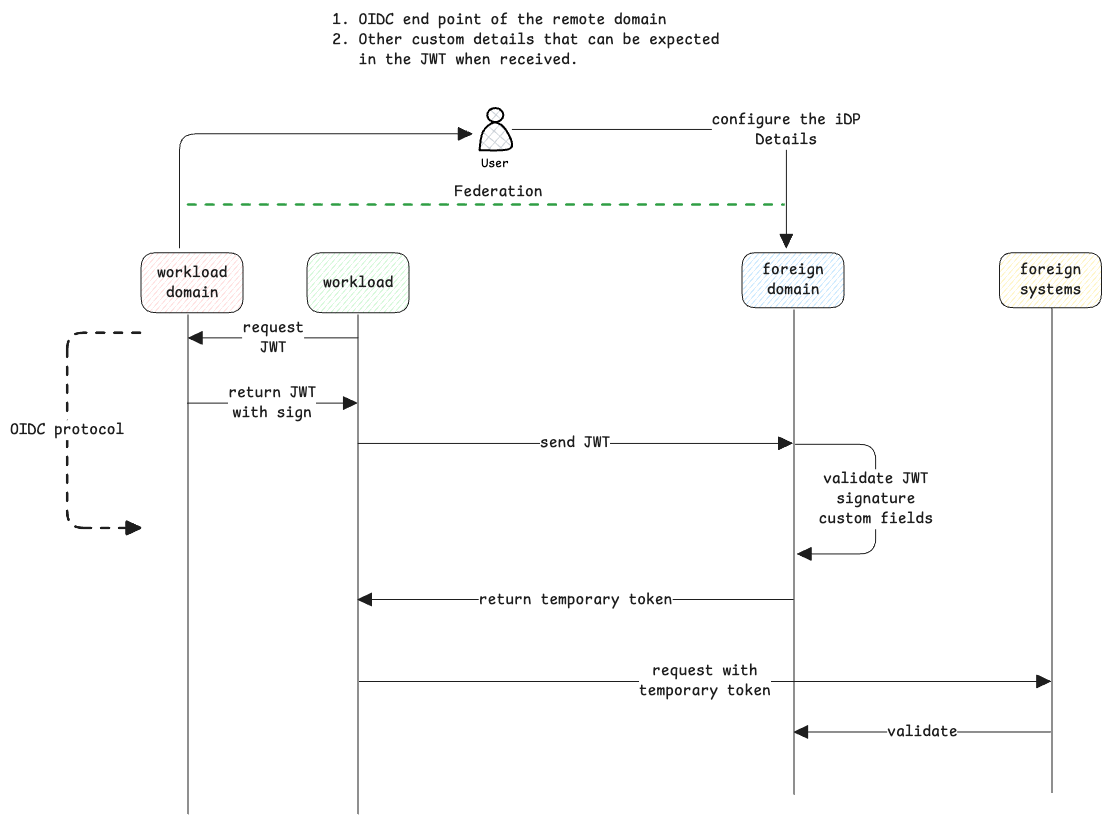
Workload Identity Federation
Workload Identity Federation lets services use short-lived credentials instead of long-lived service account keys.
Meaning of the terms
- Workload - A machine or service that runs in another trust domain.
- Identity Federation - One domain trusts an ID from another domain.
How's federation achieved?
Federation is set up by adding the other domain's identity provider as a trusted provider.
Signature is used to trust the source
When a system gets a JWT, it checks the token's signature. It gets the public key from the OIDC URL configured when the OIDC was set up. It also checks the token's issuer, audience, and expiry. The entire JWT is still in plain text.
How the domain is identified?
The remote domain can have federations with multiple domains. It uses the iss key in the JWT to identify the actual domain that's sending the JWT.